How to Build Fintech Payment Infrastructure: Architecture, Security, and Regional Strategies
Secure, scalable payment infrastructure for FinTech depends on choices about stack components, architecture, PCI-compliant data handling, and regional operations. Learn how fintech companies can design and scale each layer step by step, with the trade-offs for reliability, security, and growth.
February 02, 2026
Payment infrastructure has moved from a backend concern to a core product and risk differentiator for FinTechs. Rising transaction volumes, real-time user expectations, stricter compliance regimes, and regional fragmentation are forcing teams to rethink how payments are architected, secured, and scaled.
This article provides a step-by-step guide to building payment infrastructure for fintechs that can evolve with regulatory pressure, withstand provider failures, and support expansion into new markets without constant rework.
What Does "Payment Infrastructure" Mean In A FinTech Context?
Fintech payment infrastructure refers to the foundational systems, networks, protocols, and technologies that enable secure, efficient electronic money transfers between parties, such as consumers, businesses, and financial institutions.
In practice, payment infrastructure links several layers of fintech infrastructure into one working flow. These layers handle authorisation, settlement, reconciliation, and reporting, often in real time. Fintech companies rely on this setup to keep payments stable as volume grows.
In the wider fintech ecosystem, payment infrastructure also acts as a connector. It ties your platform to banks, card schemes, wallets, and local payment rails. This connection lets you operate across regions without rebuilding your full stack each time.
Core Components Of A Fintech Payments Stack
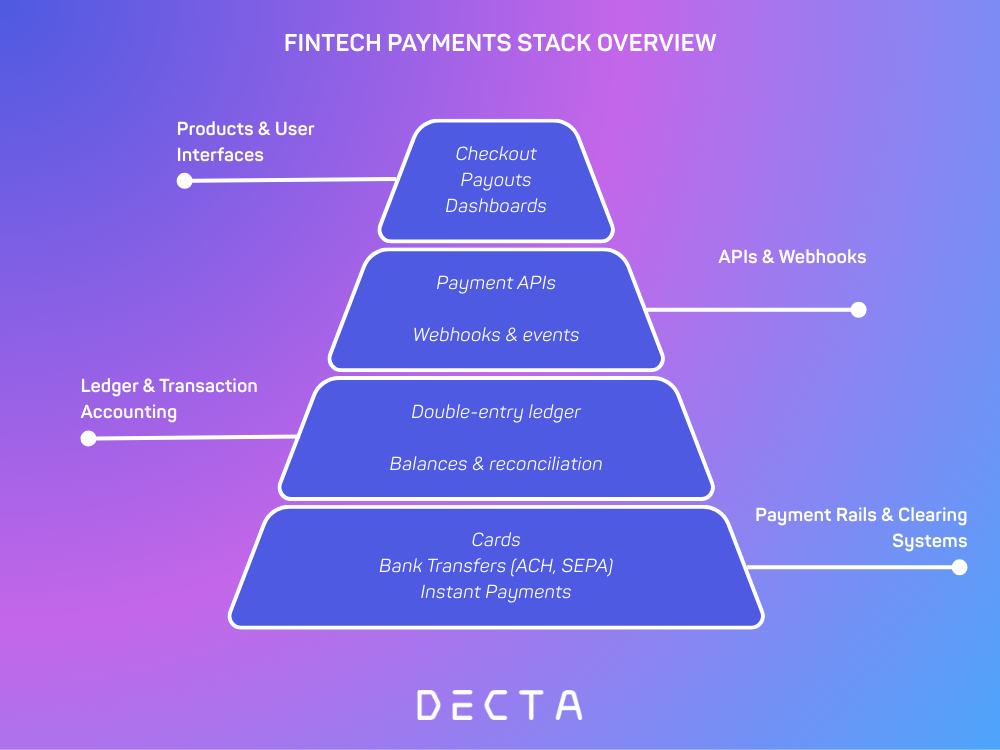
A contemporary fintech payments stack relies on robust payment processing, an accurate ledger, and explicit integration points. Each layer must operate at scale, precision, and in real time without adding fragility.
Payment Rails And Local Clearing Systems
Payment rails and local clearing systems are the building blocks for payment processing over cards, ACH transfers, and instant payment systems. You interact with:
Card schemes: Visa and Mastercard
Bank rails: ACH, SEPA or BACS
Instant payment systems: Faster Payments or RTP
Each has its own settlement windows, costs, and failure scenarios.
Instant schemes settle in seconds and payments cannot be recalled through the scheme, so your ledger and fraud checks need to run in real time before funds move.
To accept card payments, you also need an acquirer: a licensed institution with Visa or Mastercard membership that settles card funds to you. A payment processor sits between your platform, the acquirer, and the card schemes, handling authorisation, clearing, and settlement messages, so the processor you choose shapes your uptime, routing options, and time to market.
First, decide whether to interface with local clearing systems via a processor or directly. Direct integration gives you more control over fees, data, and routing but costs more in terms of build and maintenance.
Abstraction layers are easier to work with and get you to market faster, but they have limitations around logic customisation and regional optimisations.
If you are doing cross-border payments, you also have to deal with FX, correspondent banks, and local regulations. These affect cost, settlement speed, and the user experience.
Ledger And Transaction Accounting Layer
The ledger and transaction accounting layer records all the money flows on your platform.
You use double-entry bookkeeping to ensure all transactions are balanced.
This makes error detection easier.
You need to distinguish operational from accounting balances.
Operational balances capture any real-time activity such as pending authorisations or holds. Accounting balances are settled positions that can be audited for reporting.
A robust ledger supports:
Idempotent transaction posting
Immutable entries with timestamps
Reconciliation with payment processors and banks
APIs, Webhooks, And Integration Layers
APIs, webhooks, and integration layers provide an API-first architecture and keep everything in sync.
You expose external APIs for payments, payouts, and account actions. Internal APIs manage risk checks, ledger updates, and routing decisions.
Next, make your APIs versioned, well-documented, and strict about input validation to protect the core systems and allow future changes.
Then use webhooks to push real-time events like payment success, failure, chargebacks, etc. This updates downstream services without polling.
The integration layer covers retries, timeouts, and rate limiting for requests. These features help prevent cascading failures under peak load or when third parties are down.
Launch Your Own Branded Payment Gateway
DECTA White Label Payment Gateway gives fintechs a ready-made gateway with built-in payment methods and connections to DECTA or third-party acquirers.
Architecture Options For Fintech Companies Building Payment Infrastructure
The architecture options you choose for payments infrastructure for fintech platforms define the implementation of features, risk, burden and rate of traffic you can scale to. They affect your rate of iteration, compliance burden, fault isolation and permit changes to be made to your flows without breaking your service.
Monolithic Vs. Modular Architectures In Early-Stage FinTechs
The use of monolithic and modular architectures in early-stage FinTechs defines the coupling of your payment logic, data and services. Monolithic system architectures couple your checkout, risk, ledger and settlement processes to a single application and database.
You enjoy rapid feature implementation, easy testing and fewer requirements for deploying your code.
The downsides arise when you see a high volume of traffic or when your business rules are changing often. You have to ship significant changes for minor adjustments. Payment issues affect the functioning of unrelated processes. Compliance changes also necessitate sweeping changes to the code base.
A modular architecture breaks this monolith into domains, such as payments, ledgers and risk. Start by splitting read-only services or reporting into its own domain. Then separate domains that need write access (like authorisation) by using stable APIs for each domain.
Factor
Time to launch
Change isolation
Long-term flexibility
Monolithic
Fast
Low
Limited
Modular
Moderate
High
Strong
Microservices Architecture For Scalable Payment Systems
Microservices architecture for payment systems operates with a distinct boundary for each service in your system. You typically have microservices for payments, user accounts, ledgers, fraud detection and reconciliation. Each microservice owns its own data and has a public API.
This architecture style allows you to horizontally scale the system for high loads during peak activity for a particular microservice. For instance, you can scale payment authorisations without needing to scale reporting tools used by the back office.
You can also evolve and ship changes for a single microservice without redeploying your entire platform for a single team.
The downside of this higher operational complexity. You have to handle service discovery, monitoring and secure inter-service communication. Distributed transactions replace database joins, so you have to handle eventual consistency. In regulated use cases, this introduces the challenge of each microservice having audit logs and access controls.
Event-Driven And Asynchronous Processing Models
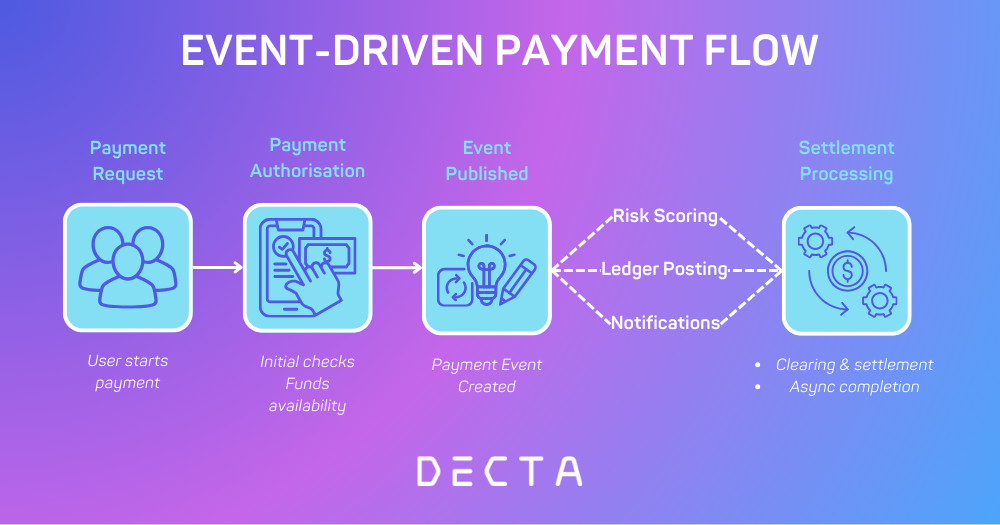
Event-driven and asynchronous processing models enable high-volume/high-concurrency payment flows. You decouple payment flows by publishing events such as payment authorised or settlement complete. These can be consumed by consumers of the events without blocking the payment process.
Asynchronous operations prevent cascading failures and reduce latency. You have to consider how consumers will safely handle duplicate events; hence, you should account for dead letter queues or idempotent keys to avoid double-charging your customer if something goes wrong.
A dead letter queue holds events that fail processing so they can be inspected and replayed safely, while an idempotency key lets a service recognise a repeated request and return the original result instead of charging twice.
Event-sourcing methodology stores changes as an immutable sequence of events, whereas traditional databases update rows in a mutable fashion. This is better for audit and replay capability, but less of a challenge for storage and querying.
Traditional state mutation updates records, but is easier to operate, and you generally find both methodologies are used; events are created for the workflow, but a different read model is used for reporting.
Designing PCI-Compliant Token Storage For FinTechs
Designing PCI-compliant token storage for FinTechs requires data minimisation, encryption and careful control of who sees payment data. You also have to manage audits, consent and ongoing compliance without adding friction to payment flows.
PCI DSS Requirements Every FinTech Must Understand
PCI DSS rules for token storage kick in as soon as you store, process or transmit card data. You need to minimise the cardholder data you hold and decide how long to keep it for. PCI DSS Requirement 3 says you cannot store sensitive authentication data, such as CVV, after authorisation.
You must make primary account numbers unreadable with encryption or tokenisation, or both. Everything you store must live in a PCI-compliant environment with access controls.
You need to validate your PCI DSS compliance every year by passing assessments, scans and attestations. The method depends on your merchant level.
If you operate in the EU or UK, GDPR requires you to manage user consent for stored card data and allow it to be revoked. You must also detect personal data breaches and report them to the supervisory authority within 72 hours.
Tokenisation Models For Card And Payment Data
Tokenisation techniques for card and payment data replace sensitive card numbers with non-sensitive tokens that hold no value outside your systems. Tokenisation limits your PCI scope and the impact of a breach.
Common tokenisation techniques include:
Gateway tokenisation: a PCI Level 1 service provider stores cards.
Vault-based tokenisation: a secure vault is used to issue tokens.
Format-preserving tokens: for legacy systems that need fixed-length tokens.
Choose a technique that stops raw card data hitting your back end. Client-side and direct-post tokenisation flows limit the exposure of card numbers at entry points. Tokens must be useless without access to the secure service that maps them.
Card schemes also issue network tokens through Visa Token Service (VTS) and Mastercard Digital Enablement Service (MDES). Network tokens replace the card number at scheme level, power wallets such as Apple Pay and Google Pay, and stay valid when a physical card is reissued, which keeps card-on-file and recurring payments working.
Secure Storage, Access Controls, And Auditability
Secure storage, access controls and auditability underpin PCI-compliant token storage operations. You need to store encryption keys separately to vaults and rotate them on a schedule.
Access controls must be least-privileged and use multi-factor authentication for operators. Avoid shared accounts and log all system access.
Auditability requires continuous logging, timestamps and tamper-proof logs. You need to preserve evidence for PCI assessments and partner queries. A well-designed audit trail helps with breach investigations and reporting to regulators without disrupting live payment processes.
Regional Strategies: Multi-Region Infrastructure And Local Payment Methods
You increase conversion and the resilience of your system if you support local payments, local infrastructure, and isolate transactions from provider outages. Payment design is an integrated operation that involves user experience, compliance, and fault tolerance.
Considerations When Designing For Regional Payment Preferences
Designing for regional payment preferences means supporting payment methods that users already rely on in the region:
UPI is the leading real-time bank payment method in India.
Pix and Boleto matter in Brazil.
iDEAL still has significance in the Netherlands.
Treat them as the base layer.
In Europe, open banking under PSD2 enables account-to-account (A2A) payments, which move money directly between bank accounts without card scheme fees. A2A gives you a lower-cost alternative to cards, especially for high-value transactions and payouts.
Next, implement a unified payments interface to standardise all payment flows and use one API, so your product teams only have to implement features once instead of accommodating cards, wallets, and local bank payments.
You will still design a front-end experience that adjusts to the region for language, currency, and field formatting.
Limit payment methods in each region to a handful of high-volume options. The more payment methods there are, the more friction there is and the longer checkouts take. Track drops, approvals, and retries for each method and use this data to improve methods over time.
Multi-Region Infrastructure And Data Residency
Multi-region infrastructure and data residency choices influence latency, reliability, and regulatory risk. Process payments as close to the user as possible to minimise authorisation delays and improve success rates. The latency of mobile checkouts can destroy conversions.
Use an active-active or active-passive structure for your multi-region infrastructure based on your size and risk exposure. Active-active improves speed and resilience but complicates data consistency and costs. Active-passive is easier to work with, but exposes your users for longer during failovers.
Comply with data residency rules per region. Tokenise payment details to avoid data residency issues when sharing data between regions. Treat logging, backup and storage the same as your data residency rules.
Failover, Redundancy, And Provider Abstraction
Failover, redundancy, and provider abstraction keep the revenue engine going when payment providers misbehave or fail. Don't couple any business logic to a single bank or gateway. Always abstract providers through your internal services with a predictable request and response structure.
Use smart routing through a payment orchestration layer, which manages multiple providers behind one integration, to send requests to payment providers by region, method, cost, and real-time performance. For example, send UPI requests to the best-performing provider available. Use retry logic with backoff to avoid duplicate payments or overloading networks.
Always have at least two payment providers for high-traffic regions and methods. Test failover routes under real-world conditions, not just in theory. Watch latency, error rates, and timeouts so your system can switch routes without impacting users.
When selecting processors, check their uptime SLA: a 99.99% commitment, common among payment infrastructure providers, still allows roughly 52 minutes of downtime a year.
Security, Compliance, And Risk As First-Class Infrastructure Concerns
Security, compliance, and risk are essential topics in payment infrastructure, as they relate to your approach to building, operating, and scaling your platform payments infrastructure. You'll want to secure payment data from collection to storage with encryption, tokenisation, and access control throughout this process.
Compliance governs how you operate your infrastructure and data. You'll want to comply with PCI DSS for card payment, GDPR for personal data, and other local regulatory bodies.
RegTech solutions can handle reporting, compliance control verification, and policy updates without interfering with your development cycles.
Identity checks help prevent fraud and regulatory non-compliance. Integrate KYC and AML checks at the start of the payment process to ensure users are legit. AML screening against sanctions and PEP lists, plus ongoing transaction monitoring, is what regulators expect from licensed payment firms.
Fraud prevention and risk scoring should occur in real-time. Use transaction data, behavioural patterns, and device information to prevent fraudulent transactions before they settle. A solid fraud prevention strategy helps you avoid chargebacks and protects your customer base and merchants.
Security and risk management best practices can include:
Fraud detection with real-time alerts
Fraud prevention and risk scoring integration into payment flows
Identity checks and KYC processes as part of the user onboarding
Security audits and routine penetration testing for vulnerabilities
For continued compliance with security, you can implement rigorous management techniques. You'll want to log access attempts and permission settings actively and perform routine audits.
3D Secure And Strong Customer Authentication
In the EU and UK, PSD2 requires Strong Customer Authentication (SCA) for most online card payments, which means verifying the customer with two of three factors: knowledge, possession, or inherence. For card payments, SCA is delivered through 3D Secure 2 (3DS2), which sends transaction and device data to the issuer so low-risk payments can pass without a challenge.
Build 3DS2 into your checkout flow and apply SCA exemptions, such as low-value or transaction risk analysis exemptions, to reduce friction on legitimate payments. Without SCA support, issuers in the EEA can soft-decline online card payments that lack authentication.
Fraud Prevention And Risk Scoring Integration
Fraud prevention and risk scoring integration is a key layer of protection in payment processing infrastructure for fintech companies. You'll want to use systems that assess every transaction's risk before funds are captured in real-time.
You can combine rule-based checks with machine learning algorithms to score payment flows. Rule-based systems are ideal for known threats, such as blacklisted countries or velocity checks. Machine learning algorithms can discover new fraud attempts in the data on your transactions based on devices used and transaction history.
Signals to include in risk scoring can be:
Transaction data: Frequency, amounts, and times
Device data: Device used for the transaction
Location data: Where the transaction has come from
Network data: The network the payment source used
You can implement a risk score for all payments. You should let low-level payments through without any delay. Medium-level payments should go through with additional step-up checks, while high-risk payments should be flagged or denied.
Use AI systems to score all payments in a matter of milliseconds to avoid delays at checkout for users. This practice minimises instances of false-positive scores that annoy users.
You'll want to structure your architecture to allow for integration without friction. You can use APIs and a microservices architecture for fraud detection models, allowing adjustments without introducing infrastructure updates that affect payments.
Build Your Payment Stack with DECTA
DECTA provides acquiring, issuing, processing, and gateway infrastructure, backed by PCI DSS Level 1 certification and 99.99% uptime.